
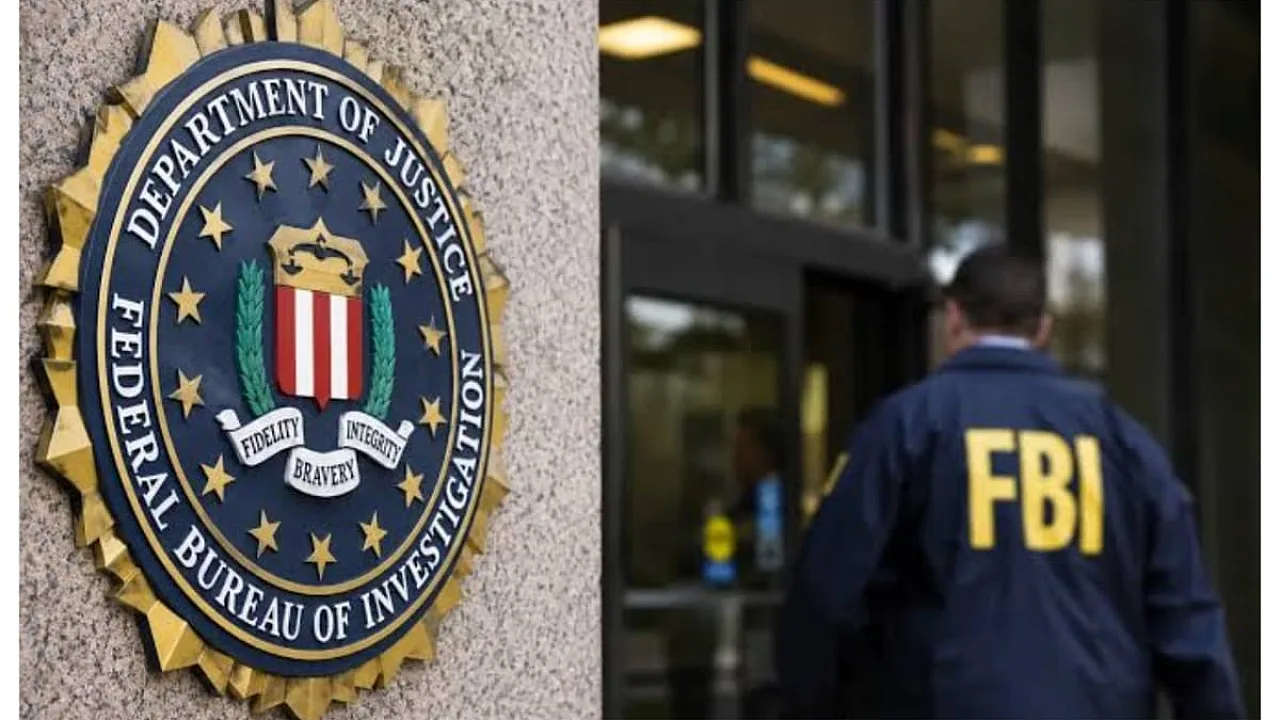
The Federal Bureau of Investigation is investigating a suspected cyberattack on its National Crime Information Centre (NCIC), a nationwide database used by law enforcement agencies across the United States to share criminal justice information. Two people briefed on the investigation told CNN that hackers apparently gained access to the system, according to reporting by CNN on Friday.
The NCIC serves as a central information-sharing platform for federal, state and local law enforcement agencies, providing access to records on outstanding warrants, wanted individuals, criminal histories and information used for background checks. A former FBI cybercrime investigations official warned CNN that the concern extended beyond whether hackers accessed sensitive information to whether they could compromise the accuracy of records used by police officers.
The suspected breach marks the second reported cyber intrusion involving FBI systems in recent months. It follows a September breach of an FBI recruitment website by the digital extortion group ShinyHunters, which reportedly exposed personal information belonging to current and former bureau employees.
The identity of those responsible for the latest suspected intrusion, the method used to access the NCIC and whether any information was stolen or altered remain unclear. The FBI did not immediately respond to requests for comment from CNN and Reuters.
The suspected breach comes amid growing concerns over cybersecurity vulnerabilities affecting US government institutions and critical infrastructure, following disruptions involving banks, the National Security Agency and the Federal Aviation Administration's air traffic control systems. FBI Director Kash Patel appeared on Fox News on Thursday to discuss the bureau's cybersecurity efforts, promoting Operation Winter Shield, an initiative aimed at encouraging organisations to strengthen their digital security and protect critical infrastructure.
Comments (0)
Leave a Comment
No comments yet. Be the first to share your thoughts.